
Partial Jailbreak of Switch 2 Discovered via SmileBasic Exploit
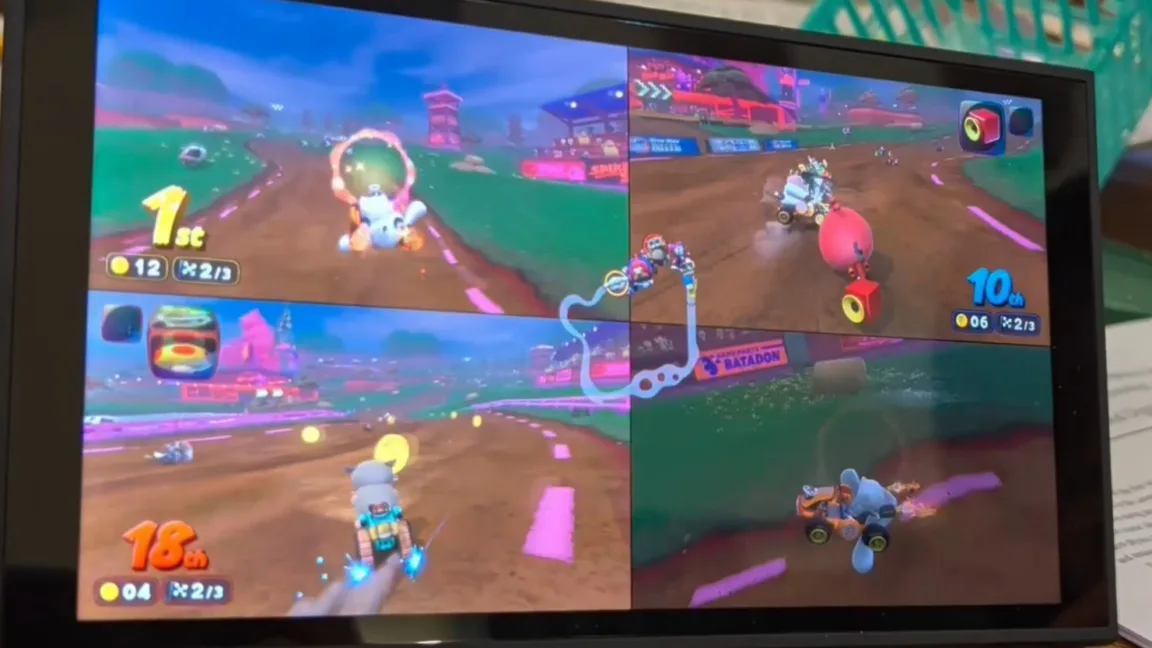
Image: Ars Technica · Source
A security researcher has demonstrated a userland exploit for Switch 2 based on an integer overflow in SmileBasic, allowing homebrew and game mods but limited to non-kernel privileges.
Less than two years after the launch of Nintendo's Switch 2, security researcher Sammy Hajhamid revealed a significant software-only partial jailbreak. This userland exploit leverages a 32-bit integer overflow vulnerability found in the interpreter for SmileBasic 4, a programming environment available on the console. Through this flaw, Hajhamid achieved read and write capabilities to portions of the system memory, enabling homebrew execution, game modification, and backup of save files.
The exploit requires a tethered setup involving a macOS or Linux PC on the same network running a node.js package to elevate system access. Hajhamid utilized OpenAI's Codex to analyze the SmileBasic interpreter, eventually uncovering the integer overflow triggered when removing items from an array. This granted an entry point into the system's memory. Further investigation led to a buffer overflow in the Switch 2's FileSystem services module. By exploiting this, Hajhamid attained arbitrary read and write privileges and was able to perform privileged filesystem actions, culminating in native code execution via a faked filesystem process.
As proof of concept, Hajhamid showcased modded characters in Mario Kart World and others in the community are developing tools and demos utilizing the exploit's capabilities. Despite these advances, the current jailbreak remains confined to userland, lacking kernel-level access necessary for full hardware control.
Notably, the SmileBasic title was removed from the Switch eShop worldwide shortly after the discovery to mitigate dissemination, though a Japanese demo version remains accessible. This strategy echoes Nintendo's response to a similar exploit on the 3DS in 2016, which also involved SmileBasic. Other exploits targeting different games are reportedly emerging within the Switch 2 hacking community.
While this vulnerability is set to be addressed in upcoming firmware updates, with version 23.0.1 being the last affected release, it represents a serious challenge to Nintendo’s system software security. Unlike the original Switch exploit from 2018, which was unpatchable and necessitated hardware redesign, the current issue can be mitigated via software patches.
The discovery underlines the ongoing contest between console hackers and manufacturers, highlighting that Nintendo’s efforts to secure their systems remain a continuous endeavor. For the Switch 2 ecosystem, this userland jailbreak marks a milestone but also signals the potential for future vulnerabilities and exploits.
Sources and original reporting
Read the original source ↗
Comments (0)
No comments yet. Start the discussion.
Write a comment
Comments are published after moderation. Your name and comment will be visible publicly. Account