
Energize Lab Responds to Security Flaws in Eiliko Robot with Independent Review
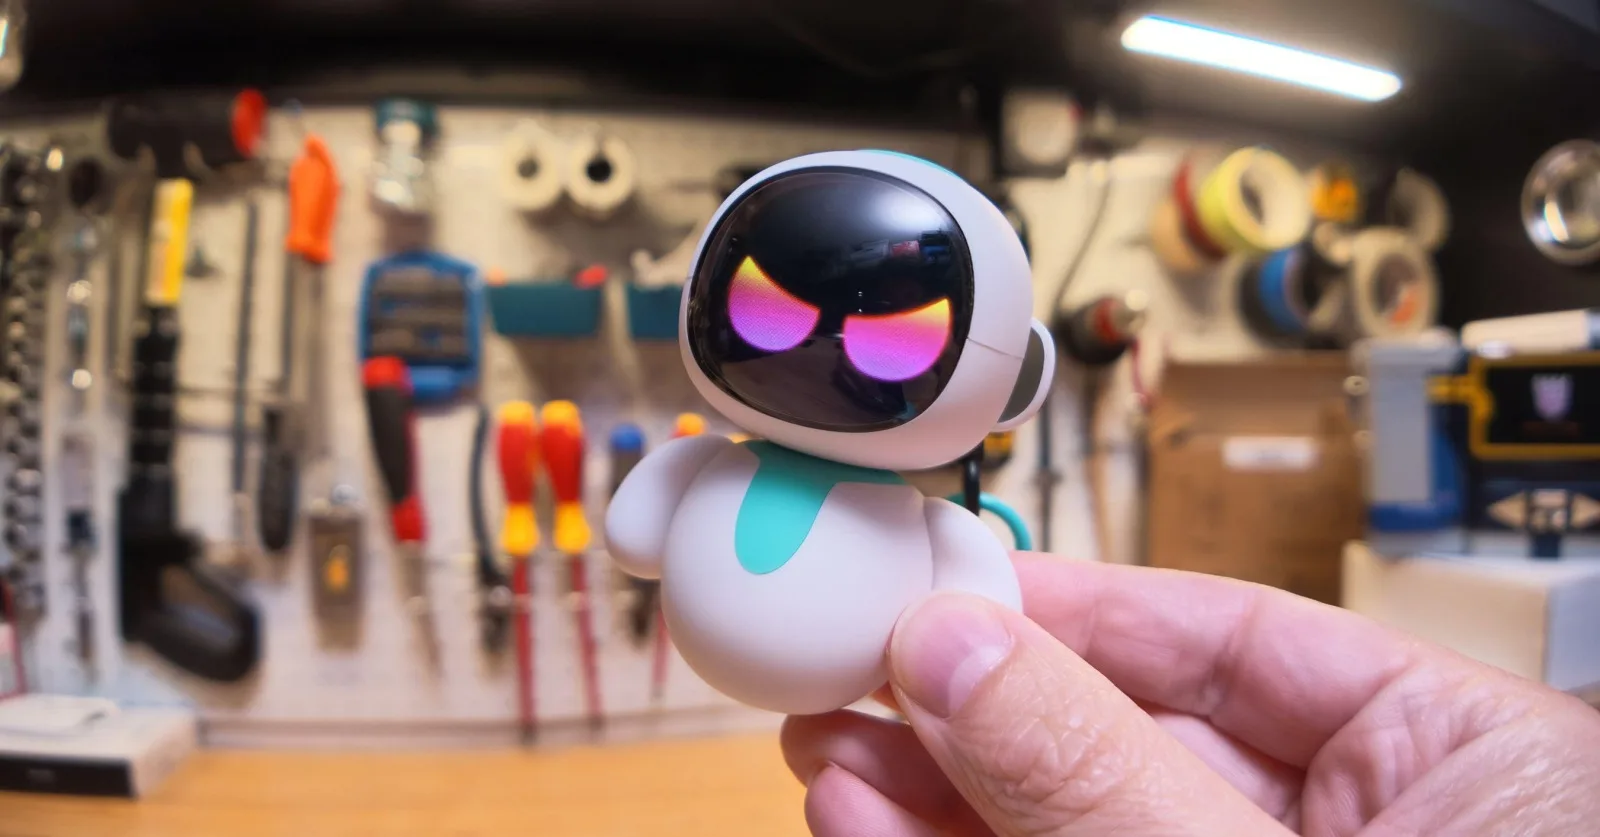
Image: Eiliko maker says it’s hiring an “independent security firm’ after Verge report on its insecure robots · Source
Following reports exposing vulnerabilities in the AI-powered Eiliko robot charm, Energize Lab commits to an independent security audit and immediate measures to secure user data and system access.
Energize Lab, the company behind Eiliko — a small AI-enabled robot charm designed to engage users in conversation — has acknowledged serious security vulnerabilities after a detailed investigation highlighted significant privacy risks. The robot, marketed to reassure users that their conversations were confidential, was found to have multiple exploitable weaknesses that would allow unauthorized access to sensitive user data. This critical situation came to light following a prolonged effort by The Verge and security researcher Sammy Azdoufal to communicate with the company, which initially went unanswered.
In a statement provided after weeks of silence, Energize Lab confirmed they had verified the main security problems outlined in the reporting and outlined steps to address them. Key immediate actions include closing all external backend system access, revoking access credentials, and disabling the web interface that allowed remote modifications of the robot’s responses. The company has also taken offline features such as the robot’s long-term memory and custom avatar functions, pledging to stop storing conversation records and user profiles to mitigate privacy concerns.
Importantly, Energize Lab announced it would delete all previously collected data, including conversation logs, profiles, and avatar images. However, the firm indicated that some level of data collection via long-term memory and custom avatars could return, but only after a thorough security review by an independent firm confirms the features are safe. To oversee this process, Energize Lab has engaged an external security auditor to conduct a full system evaluation.
Despite these measures, independent verification reveals continuing vulnerabilities. The journalist and researcher confirmed that, as of the company’s statement, audio recordings and user photos were still accessible on unsecured public web addresses. Additionally, Azdoufal maintained SSH access to the robots, allowing potential manipulation and transcript access. These ongoing risks suggest the company’s claim of eliminating external access was premature.
Energize Lab apologized for the delay in responding to the security concerns and has established a dedicated security contact email to better monitor issues going forward. The company emphasized the importance of regaining user trust and committed to transparency during the remediation process.
The Eiliko robot initially aimed to bring joy through interactive AI companionship, but the lack of robust security significantly undermined that goal. Energize Lab’s forthcoming independent security review and data handling reforms will be critical steps toward restoring confidence in their product’s safety and privacy safeguards. The company plans to provide progress updates as they work to resolve these serious issues.


Sources and original reporting
Read the original source ↗
Comments (0)
No comments yet. Start the discussion.
Write a comment
Comments are published after moderation. Your name and comment will be visible publicly. Account