
Massive Data Leak Reveals Identities of 41,000 DHS Personnel Including Undercover ICE Agents
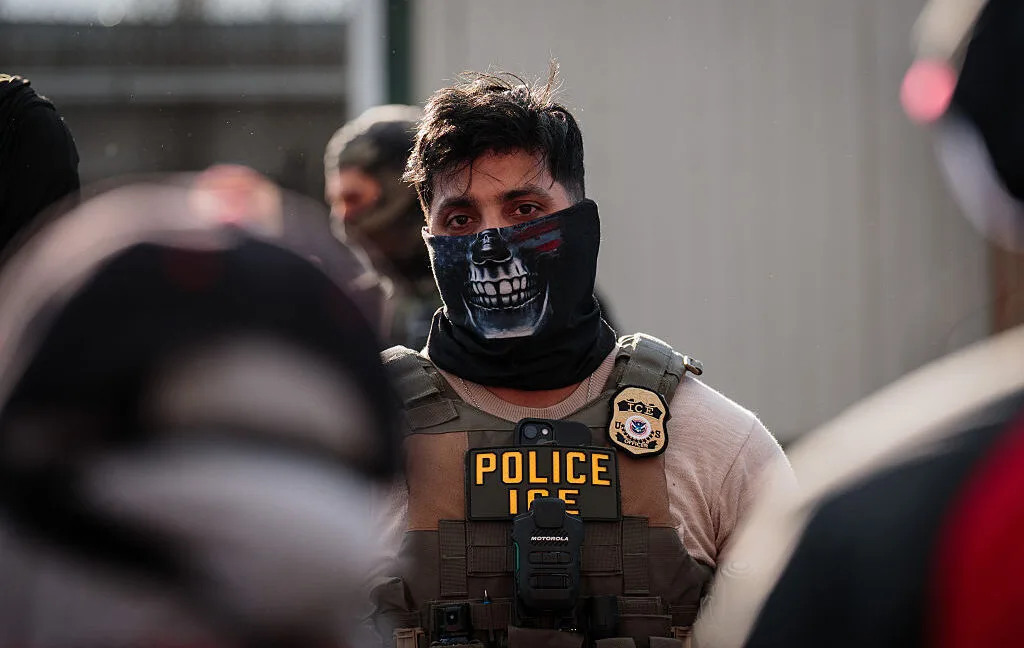
Image: Ars Technica · Source
A significant leak exposing over 41,000 Department of Homeland Security employees, including undercover ICE agents and internal surveillance program details, raises concerns about security and transparency.
In October 2026, a major leak of internal Department of Homeland Security (DHS) data has come to light, revealing detailed information on more than 41,000 employees and contractors across DHS and its component agencies. The leaked archive, known as "Icepick," was published by the transparency organization Distributed Denial of Secrets (DDoSecrets) and includes sensitive details such as email addresses, phone numbers, office locations, and references to covert programs within DHS. The data spans DHS as well as seven sub-agencies, including Immigration and Customs Enforcement (ICE) and US Customs and Border Protection (CBP).
The source of the data is believed to be DHS’s Okta login system, which manages employee access to internal services. Okta has denied any evidence of a breach on its systems. The leaked records expose not only contact information but also internal permission group memberships, revealing involvement in undercover and surveillance operations. These groups reference tools and programs such as the Certified Undercover Operation (CUC), Communications Intercept Center TechOps (CICTO), Title III wiretap intercept programs, and sensor interception initiatives.
The leak highlights groups associated with facial recognition apps, encrypted communications apps like Signal, and investigative platforms including Palantir Falcon and PenLink. Notably, certain permission groups labeled "Executive Leadership" and "AI Access" list high-ranking officials and former DHS leaders, with access exemptions to DHS web filtering. The documents also reference the use of AI tools from OpenAI, Google, and Microsoft within DHS internal systems.
According to analysis, CBP personnel constitute the majority of the records, with ICE employees comprising about 10,000 entries, including investigators and enforcement officers. The archive also details involvement from contractors and affiliated personnel, providing insight into the DHS organizational structure from top leadership to field agents as well as local law enforcement authorized to perform immigration functions.
Security experts warn that such detailed exposure could be exploited by adversaries to identify vulnerable personnel, impersonate employees, or compromise ongoing DHS investigations. The leak arrives amid increasing DHS efforts to conceal employee identities, aggressive legal stances against critics, and expanded definitions of doxing concerning DHS personnel.
Homeland Security officials have acknowledged the situation and stated they are actively responding to the breach to protect employees and operations. The leak has sparked debate about government transparency versus personnel privacy, with the leak creators framing the exposure as a tool for accountability rather than malicious doxing.
This disclosure follows recent similar breaches targeting federal agencies, heightening concerns over cybersecurity practices within US government departments and the risks associated with protecting sensitive workforce and operational information.
Sources and original reporting
Read the original source ↗
Comments (0)
No comments yet. Start the discussion.
Write a comment
Comments are published after moderation. Your name and comment will be visible publicly. Account