
Bluesky Blocks Access to Leaked DHS Employee Data Amid Government Takedown Efforts
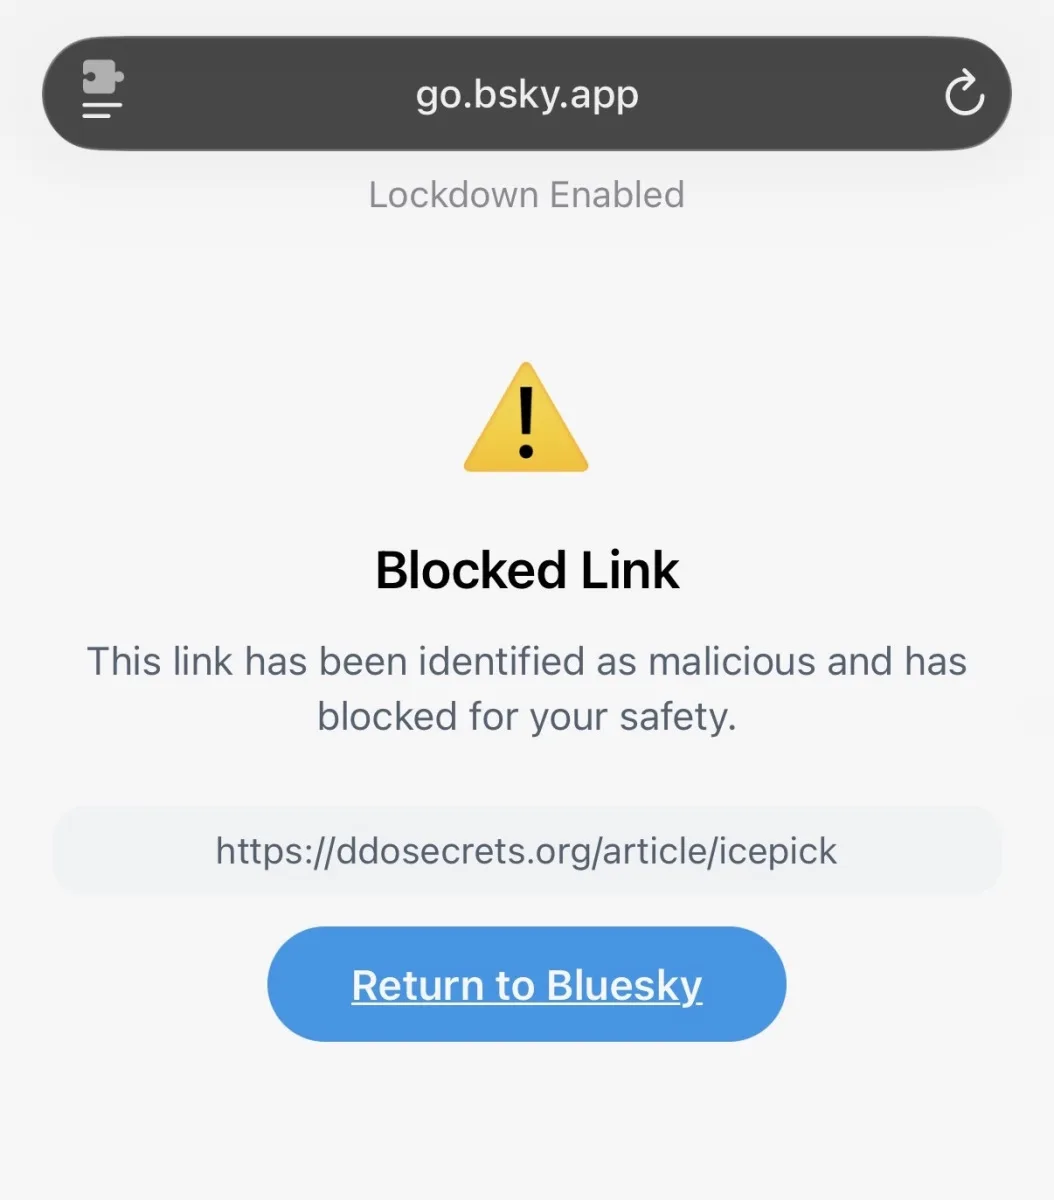
Image: A screenshot showing Bluesky blocking links to DDoSecrets.Image Credits:TechCrunch / · Source
After a major leak exposed thousands of U.S. Department of Homeland Security employee records, social network Bluesky blocked links to the hosting nonprofit site while the government pursues removal of the data online.
In October 2026, a significant data breach compromised over 40,000 user account records associated with the U.S. Department of Homeland Security (DHS). The leaked dataset, which included names, professional contact details, and work-related phone numbers of employees from agencies such as Customs and Border Protection (CBP) and Immigration and Customs Enforcement (ICE), was made publicly available by the nonprofit transparency collective DDoSecrets.
The exposed information resembled details typically found on employees’ business cards and was considered valuable by researchers investigating government activities, especially under public records laws like the Freedom of Information Act (FOIA).
Following media reports on the breach, Bluesky, a social networking platform, began blocking its users from accessing links to DDoSecrets' site hosting the leak, marking these links as "malicious." While Bluesky did not remove posts referencing the data outright, a spokesperson explained to Wired that the leaked information violated the platform’s community guidelines.
DDoSecrets co-founder Emma Best clarified that the dataset contained professional, not personal, contact information and argued its public availability serves transparency, particularly given the government’s own requirements for FOIA requests involving such data.
Meanwhile, the DHS confirmed awareness of the breach and stated that efforts to address the situation were underway. The department, through its security vendor ZeroFox, issued takedown notices demanding removal of the leaked data from the internet to the domain registrar CentralNic, which has subsequently placed an affected website on "serverHold," effectively taking it offline.
Notably, a searchable online interface created by journalist maia arson crimew to explore the data was taken down as part of these actions. However, alternative access remains possible through locally hosted versions of the dataset.
This sequence of events highlights ongoing tensions between government efforts to secure sensitive information, public interest in transparency, and platforms’ roles in moderating access to leaked data. Bluesky’s approach emphasizes content blocking over post removal, while DHS actively pursues legal and technical measures to mitigate the dissemination of the compromised records.
Sources and original reporting
Read the original source ↗
Comments (0)
No comments yet. Start the discussion.
Write a comment
Comments are published after moderation. Your name and comment will be visible publicly. Account